NexGen Governance, Risk & Compliance Virtual Summit (US Edition)
Strengthen enterprise resilience with connected governance, risk, and compliance strategies that help organizations manage regulatory change, automate controls, reduce risk exposure, and build a culture of accountability across the enterprise.
Date
3rd December, 2026Time
11:00 AM ETExperts Speakers
6+Overview
From Risk Management to Enterprise Resilience
Governance, risk, and compliance are no longer isolated functions. As organizations face evolving regulations, growing third-party ecosystems, cybersecurity threats, operational complexity, and increasing expectations for transparency, GRC leaders need connected strategies that bring risk, compliance, policies, controls, and business decisions together.
The NexGen Governance, Risk & Compliance Virtual Summit (US Edition) brings together GRC, risk, compliance, audit, legal, security, technology, and business leaders to explore how organizations can strengthen enterprise resilience through connected risk management, intelligent compliance processes, and greater visibility across the organization.
The summit will explore how organizations can:
- Build a connected approach to governance, risk, and compliance
- Identify and assess enterprise risks before they become business disruptions
- Automate compliance processes, controls, and evidence collection
- Keep pace with changing regulations and compliance requirements
- Strengthen regulatory change management across business functions
- Improve visibility into operational, financial, cyber, and third-party risks
- Manage policies, controls, assessments, and compliance obligations centrally
- Strengthen third-party and vendor risk management
- Improve audit readiness with reliable, accessible compliance data
- Connect risk insights with strategic business decision-making
- Establish accountability across risk and compliance programs
- Use technology and automation to reduce manual GRC processes
- Monitor risk indicators and compliance performance in real time
- Build a proactive risk culture across the enterprise
Organizations can move beyond fragmented spreadsheets and disconnected processes toward a more integrated GRC approach that improves visibility, strengthens accountability, and enables faster, more informed business decisions.
Why
Connect Governance. Strengthen Risk Management. Build Resilience.
Here’s why you shouldn’t miss it:
Digital Sessions
Learn from GRC, risk, compliance, audit, and technology leaders exploring modern approaches to enterprise risk, compliance automation, regulatory change, and organizational resilience.
Digital Panel Discussions
Explore practical strategies for managing emerging risks, automating compliance, strengthening third-party oversight, improving audit readiness, and connecting GRC with business strategy.
Digital Networking
Connect with governance, risk, compliance, legal, audit, security, technology, and business leaders across the US.
Virtual One-to-One Meetings
Engage with experts to explore risk management, compliance transformation, GRC automation, regulatory requirements, third-party risk, and enterprise resilience strategies.
Our
Knowledge Sessions
Experience dynamic web panel discussions, live fireside chats, and interactive digital presentations that offer in-depth insights.
Industry Leaders
Connect virtually with industry leaders, decision-makers, and experts to explore emerging trends, share insights, and discover new strategies shaping the future.
Attendees
Join a distinguished group of senior executives and industry professionals for meaningful knowledge exchange and collaboration.
Our
- Moving From Reactive Risk Management to Proactive Risk Intelligence
- Connecting Governance, Risk & Compliance Across the Enterprise
- Automating Compliance Processes and Control Management
- Managing Regulatory Change in a Fast-Moving Environment
- Strengthening Enterprise Risk Identification and Assessment
- Building Effective Third-Party & Vendor Risk Programs
- Improving Policy Management and Employee Accountability
- Connecting Risk Data With Strategic Business Decisions
- Strengthening Internal Controls and Audit Readiness
- Managing Operational, Cyber, and Emerging Enterprise Risks
- Using Automation to Reduce Manual GRC Workloads
- Building a Culture of Risk Awareness and Compliance
- Improving Visibility Across Enterprise Risk Programs
- Measuring GRC Performance and Business Impact
Key Focus Areas
- Governance, Risk & Compliance
- Enterprise Risk Management
- Compliance Management
- Regulatory Change Management
- Risk & Control Management
- GRC Automation
- Third-Party Risk Management
- Vendor Risk Management
- Policy Management
- Internal Controls
- Audit & Assurance
- Operational Risk
- Cyber & Technology Risk
- Regulatory Compliance
- Enterprise Resilience
- Risk Intelligence

WHO SHOULD ATTEND?
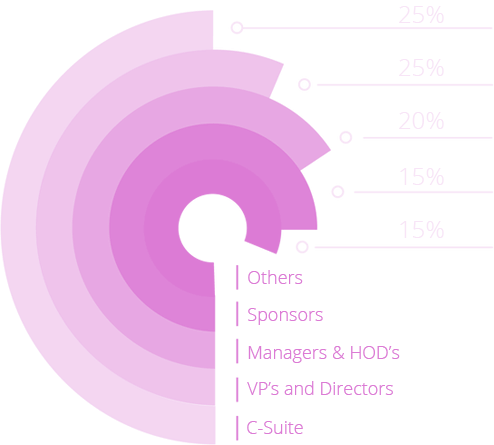
CXOs, VPs, Directors, Heads, Managers & Specialists in -
- Chief Risk Officers
- Chief Compliance Officers
- Chief Audit Executives
- Chief Information Security Officers
- Chief Legal Officers
- Heads of Governance, Risk & Compliance
- Heads of Enterprise Risk
- Heads of Compliance
- Heads of Internal Audit
- Risk & Compliance Directors
- GRC Directors
- Regulatory Compliance Directors
- Enterprise Risk Management Leaders
- Third-Party Risk Leaders
- Internal Audit Leaders
- Compliance Program Leaders
- Legal & Regulatory Affairs Leaders
- Information Security & Risk Leaders
Topics
Governance, Risk & Compliance
Enterprise Risk Management
Compliance Automation
Regulatory Change Management
Risk & Control Management
Third-Party Risk
Vendor Risk Management
Policy Management
Internal Audit
Audit Readiness
Operational Risk
Cyber Risk
Regulatory Compliance
Risk Intelligence
Enterprise Resilience
GRC Technology
Our
Banking & Financial Services
Insurance
Healthcare & Pharmaceuticals
Manufacturing
Retail & E-commerce
Technology & Software
Telecommunications
Energy & Utilities
Automotive
Transportation & Logistics
Professional Services
Government & Public Sector
Speakers


Karen Mascarenhas
Manager, Demand Generation - Uniphore
Thank you for the great session. Reimagining Customer Experiences with Proactive Customer Care

Jennifer Mavaseh
Director of Business Development -Nastel Technologies, Inc.
It was a pleasure working with you on this webinar. AIOP’s for Businesses

Elise Dumolin
Field Marketing Manager -DACH -Nintex
Thank you so much for all ur support for the event. Expense Management for Businesses

Cameron
Regional Marketing Specialist, APAC - Akeneo
Thank you again for your assistance with hosting the event and I turned in for a brief period and was very happy with how smoothly things were running.. Digital Process Automation for Businesses
Frequently Asked Questions
Where will the event be held?
This is an online event. You do not have to travel to any specific location. You can participate from your convenient location. The virtual event is accessible from a computer, mobile and tablet devices.
How do I log in on the day of the virtual event?
Your login details will be sent to you via email before the event. Use them to access the online platform.
Can I invite my colleagues and friends to attend the virtual event?
Absolutely. We are counting on you to invite others! Help us spread the word. You can simply share the link to this page, and they can register at their convenience.
