NexGen Autonomous Pentesting Virtual Summit (US Edition)
Traditional penetration testing can provide valuable snapshots, but modern attack surfaces change continuously. Explore how autonomous pentesting can continuously test real environments and uncover attack paths that scanners may miss. Discover how organizations can validate exploitability, prioritize risks by real business impact, and verify that remediation actually works. Learn how security teams can move toward continuous security validation across infrastructure, cloud, identity, Kubernetes, and web applications.
Date
15th December 2026Time
11:00 AM ETExperts Speakers
6+Overview
From Vulnerability Detection to Continuous Attack-Path Validation
Security teams face an expanding attack surface across internal infrastructure, external assets, cloud environments, identities, applications, and Kubernetes. Finding vulnerabilities is only part of the challenge. Organizations also need to understand which weaknesses can actually be chained together to create meaningful business impact.
The NexGen Autonomous Pentesting Virtual Summit (US Edition) will explore how autonomous security testing can continuously discover and safely exploit weaknesses using attacker-like techniques. The discussions will focus on attack-path validation, exploitability, remediation, and continuous security verification.
The summit will explore how organizations can:
- Continuously test internal and external attack surfaces
- Discover exploitable attack paths instead of relying only on individual vulnerability findings
- Safely simulate attacker behavior across complex environments
- Identify how credentials, misconfigurations, vulnerabilities, and security-control gaps can be chained together
- Prioritize weaknesses based on demonstrated impact and exploitability
- Validate security controls from an attacker's perspective
- Assess cloud environments, identities, and Kubernetes security
- Test web applications and understand how application weaknesses connect to underlying infrastructure
- Use automated attack-path analysis to accelerate security assessments
- Verify that remediation has actually eliminated exploitable paths
- Track changes in the exploitable attack surface over time
- Build continuous security validation into vulnerability and risk management programs
The summit will bring together cybersecurity, penetration testing, vulnerability management, cloud security, and security operations leaders to explore how autonomous testing can provide continuous evidence of what attackers can actually achieve.
Why
Find the Path. Prove the Risk. Verify the Fix.
Here’s why you shouldn’t miss it:
Digital Sessions
Explore autonomous pentesting, attack-path discovery, exploitability validation, cloud security testing, and continuous security assessment.
Digital Panel Discussions
Hear security leaders discuss moving beyond vulnerability scanning, prioritizing exploitable risks, continuous validation, and remediation verification.
Digital Networking
Connect with cybersecurity, offensive security, vulnerability management, cloud security, and security operations leaders across the United States
Virtual One-to-One Meetings
Discuss autonomous pentesting strategies, attack-path validation, remediation, and continuous security testing with industry experts.
Our
Knowledge Sessions
Experience dynamic web panel discussions, live fireside chats, and interactive digital presentations that offer in-depth insights.
Industry Leaders
Connect virtually with industry leaders, decision-makers, and experts to explore emerging trends, share insights, and discover new strategies shaping the future.
Attendees
Join a distinguished group of senior executives and industry professionals for meaningful knowledge exchange and collaboration.
Our
- Moving Beyond Point-in-Time Penetration Tests
- Finding Attack Paths Instead of Isolated Vulnerabilities
- Understanding What an Attacker Can Actually Exploit
- Chaining Credentials, Misconfigurations, and Vulnerabilities Into Real Attack Paths
- Validating Internal Security From an Assumed-Breach Perspective
- Testing External Attack Surfaces Continuously
- Assessing Cloud and Identity Attack Paths Across Hybrid Environments
- Identifying Security Weaknesses in Kubernetes Environments
- Connecting Web Application Weaknesses to Infrastructure-Level Impact
- Prioritizing Remediation Based on Proven Exploitability
- Verifying That Security Fixes Actually Break Attack Paths
- Measuring Changes in Exploitable Risk Through Continuous Testing
Key Focus Areas
- Autonomous Pentesting
- Continuous Security Validation
- Attack-Path Analysis
- Exploitability Assessment
- Internal & External Pentesting
- Cloud Security Testing
- Identity Security
- Kubernetes Security
- Web Application Security
- Remediation Validation
- Exposure Management
- Attacker-Centric Security

WHO SHOULD ATTEND?
CXOs, VPs, Directors, Heads, Managers & Specialists in -
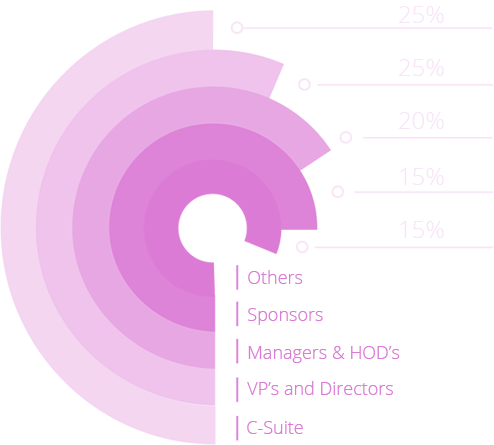
- Chief Information Security Officers
- Chief Information Officers
- Heads of Cybersecurity
- Heads of Offensive Security
- Heads of Vulnerability Management
- Security Directors
- Penetration Testing Directors
- Security Operations Directors
- Cloud Security Directors
- Application Security Directors
- Security Architecture Leaders
- Cyber Risk Leaders
Topics
Autonomous Penetration Testing
Continuous Security Validation
Attack-Path Discovery
Exploitability Testing
Internal Network Pentesting
External Attack Testing
Cloud Pentesting
Identity & IAM Testing
Kubernetes Pentesting
Web Application Pentesting
Remediation Verification
Continuous Exposure Validation
Our
Banking & Financial Services
Insurance
Technology & SaaS
Healthcare & Life Sciences
Retail & E-commerce
Manufacturing
Telecommunications
Automotive
Energy & Utilities
Professional Services
Media & Entertainment
Government & Public Sector
Speakers


Karen Mascarenhas
Manager, Demand Generation - Uniphore
Thank you for the great session. Reimagining Customer Experiences with Proactive Customer Care

Jennifer Mavaseh
Director of Business Development -Nastel Technologies, Inc.
It was a pleasure working with you on this webinar. AIOP’s for Businesses

Elise Dumolin
Field Marketing Manager -DACH -Nintex
Thank you so much for all ur support for the event. Expense Management for Businesses

Cameron
Regional Marketing Specialist, APAC - Akeneo
Thank you again for your assistance with hosting the event and I turned in for a brief period and was very happy with how smoothly things were running.. Digital Process Automation for Businesses
Frequently Asked Questions
Where will the event be held?
This is an online event. You do not have to travel to any specific location. You can participate from your convenient location. The virtual event is accessible from a computer, mobile and tablet devices.
How do I log in on the day of the virtual event?
Your login details will be sent to you via email before the event. Use them to access the online platform.
Can I invite my colleagues and friends to attend the virtual event?
Absolutely. We are counting on you to invite others! Help us spread the word. You can simply share the link to this page, and they can register at their convenience.
